Enterprise Cyber Defense Architecture

Security Operations & Threat Hunting Knowledge Base

A synchronized, interactive repository bridging reactive Level 1 Security Operations Center (SOC) incident triage and proactive enterprise threat hunting methodologies mapped to INE Security professional curriculums.

Launch eSOC Live Workspace Launch eCTHP Live Workspace
2 Specializations
Reactive & Proactive Ops
15 Courses
Structured Modular Notes
100+ Hours
Curriculum Scope Covered
100% Client-Side
Offline & Pages Ready
Defensive Tier 1

eSOC Study Hub

INE Security Operations Certified – Level 1
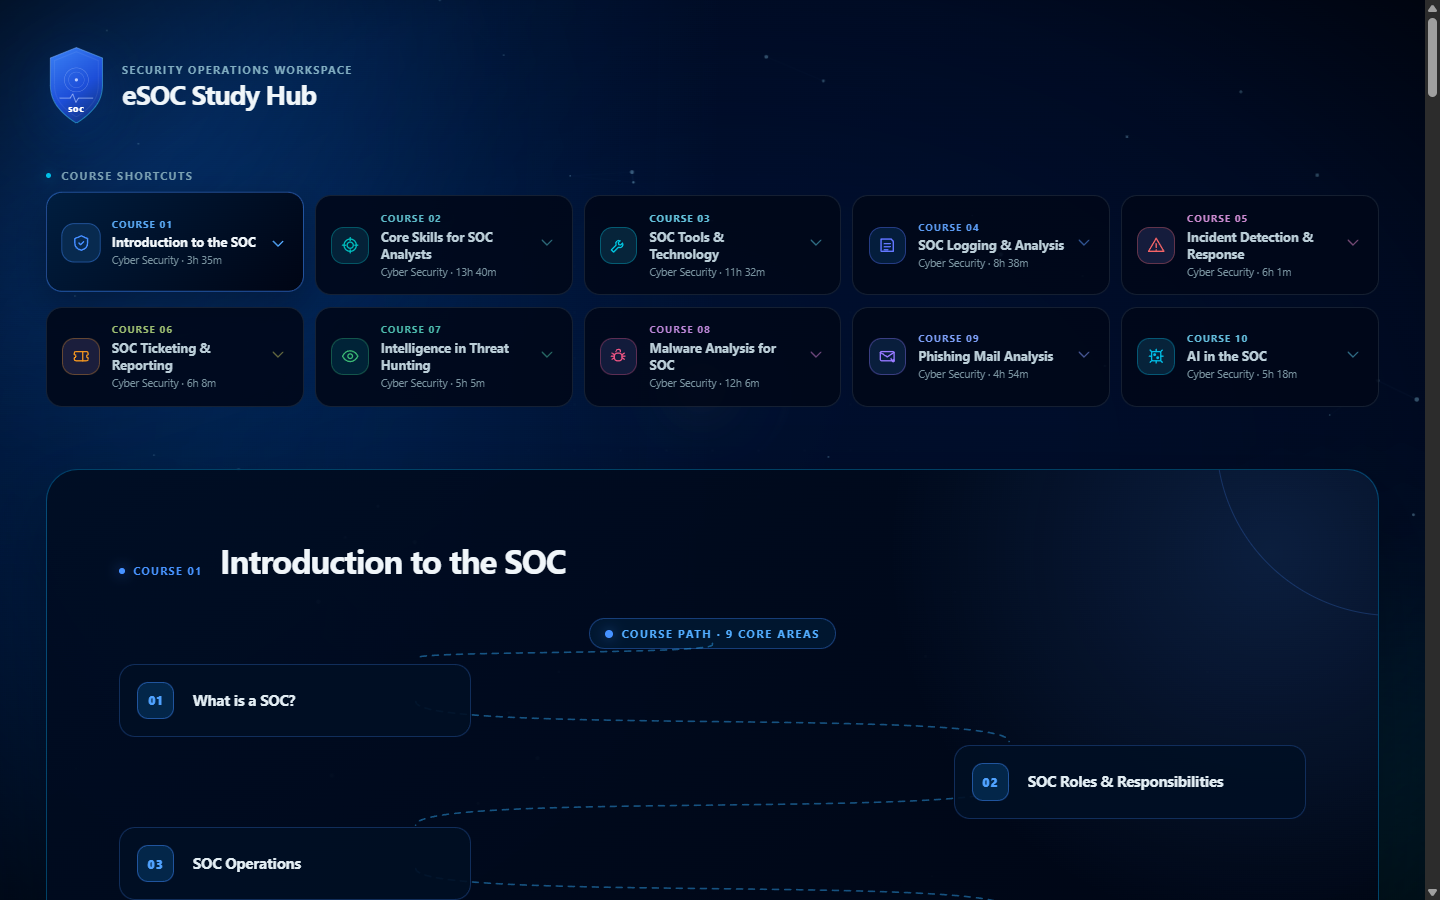
A comprehensive, modular study hub designed for frontline SOC analysts. Focuses on reactive defensive operations, continuous monitoring, security telemetry triage, alert escalation, network packet analysis, and baseline incident response workflows.

10 Courses 76h 57m Duration SIEM & Log Analysis Wireshark & TCPDump Incident Handling
  • C01 Introduction to SOC Operations04h 15m
  • C02 Network Defense Fundamentals08h 30m
  • C03 Endpoint Telemetry & Event Logs07h 45m
  • C04 SIEM Operations & Query Tuning11h 20m
  • C05 Alert Triage & True/False Positives06h 50m
  • C06 Network Packet Analysis (Wireshark)09h 10m
  • C07 Incident Response Lifecycle (NIST)08h 15m
  • C08 Threat Intelligence in Tier 105h 40m
  • C09 Forensics & Evidence Handling07h 35m
  • C10 SOC Automation & SOAR Concepts07h 37m
Threat Hunting

eCTHP Study Hub

INE Certified Threat Hunting Professional

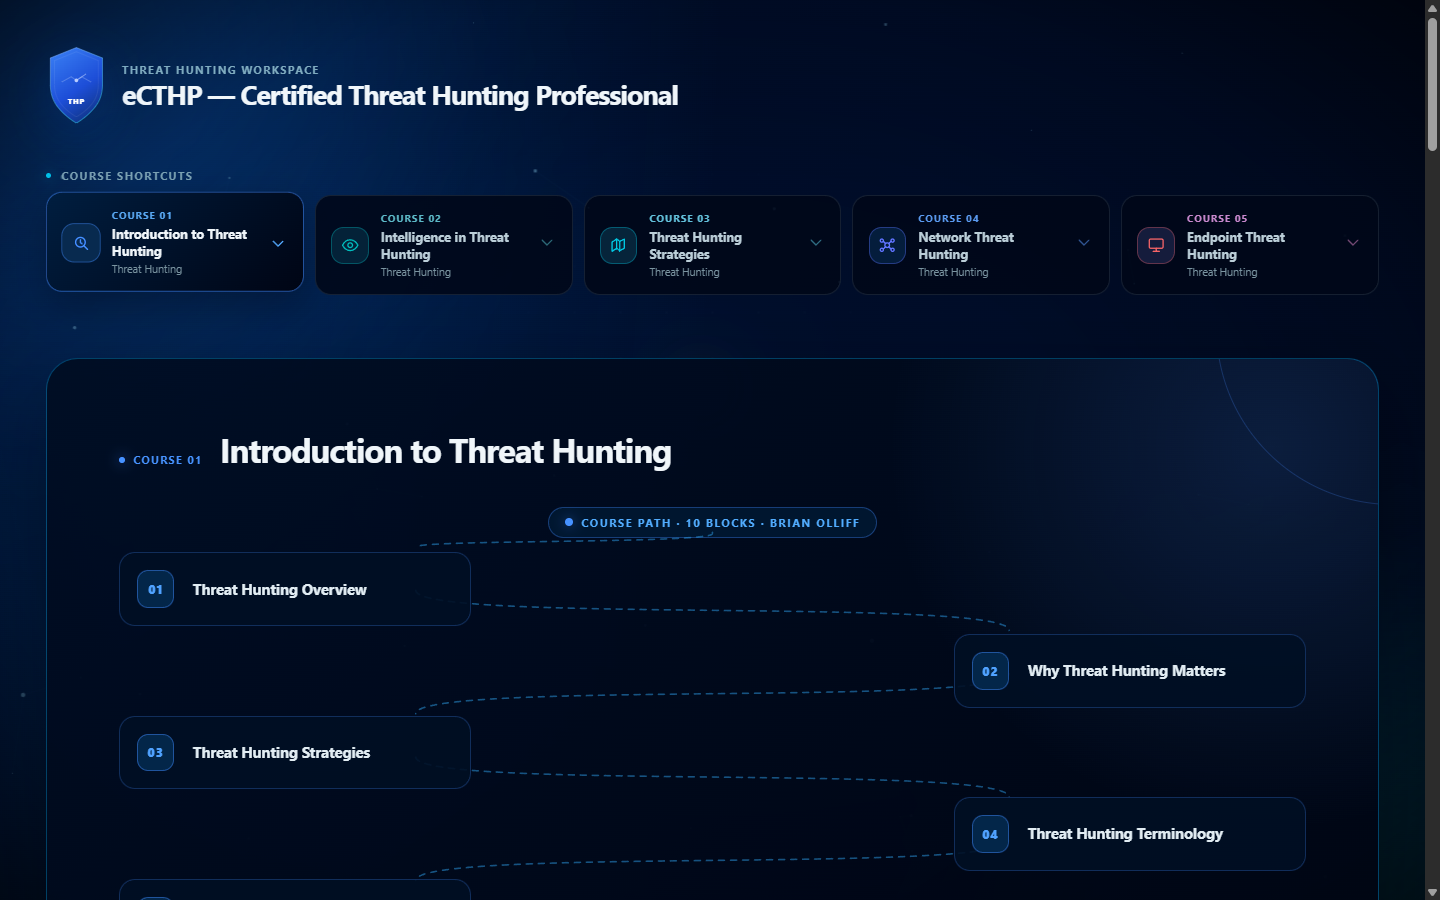
An advanced hunting portal focused on hypothesis-driven detection of advanced adversaries who evade automated defenses. Covers threat intelligence integration, hunting strategies, endpoint anomalies, memory forensics, and network beacon analysis.

5 Core Courses Hypothesis Generation Cyber Threat Intel (CTI) Endpoint Forensics MITRE ATT&CK Mapping
  • T01 Introduction to Threat Hunting & MindsetFoundations
  • T02 Cyber Threat Intelligence in HuntingCTI & TTPs
  • T03 Threat Hunting Strategies & HypothesesMethodologies
  • T04 Network Threat Hunting (C2 & Beacons)PCAP & Zeek
  • T05 Endpoint Threat Hunting & VolatilityMemory & EDR

Operational Architecture: Reactive vs. Proactive

How the two study hubs complement each other within a modern enterprise cyber defense lifecycle.

Operational Dimension eSOC Hub (Reactive Defense) eCTHP Hub (Proactive Hunting)
Primary Mindset Alert-Driven: "What triggered this alert?" Hypothesis-Driven: "Where is an attacker hiding right now?"
Trigger Mechanism SIEM alerts, automated detections, IDS signatures Threat intelligence reports, TTP patterns, anomalous baselines
Key Tooling & Data SIEM queries, PCAP analysis, EDR triage consoles Event log telemetry, memory volatility, persistence scanners
Outcome & Deliverable Triage verdict (True/False Positive), containment escalation New detection rules, gap remediation, undetected breach discovery
eSOC Live Hub Security Operations Certified – Level 1
Standalone
eCTHP Live Hub Certified Threat Hunting Professional
Standalone